 AuthBox
Every capability, beside what proves it.
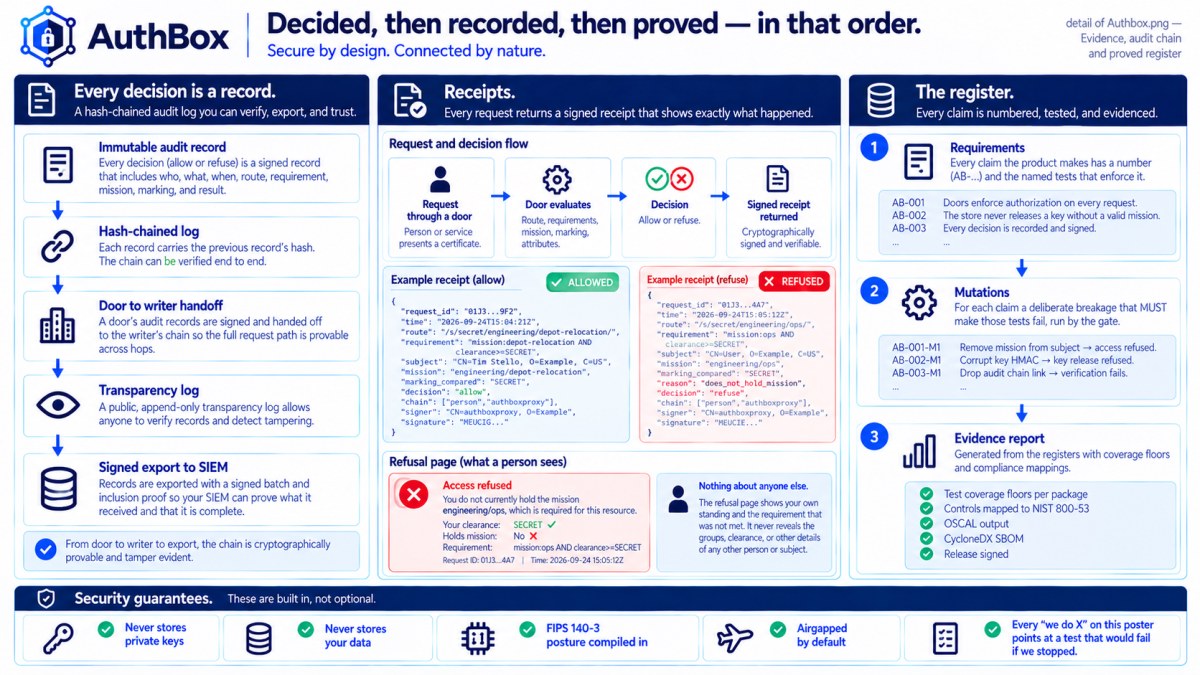
The support matrix answers what a capability touches. This answers the question after it: how much of it is proven, and by what kind of test. Nothing below is typed by hand — every cell resolves to an entry in a register or to a behaviour in the shipped rehearsal population.
rows with at least one package under a statement-coverage floor the gate holds
rows the exercise ledger reaches at any tier
rows a behaviour of the shipped population drives against a live deployment
rows whose plans carry a declared mutation proving their tests bite
rows the composed smoke names — a check line of the all-in-one bring-up that an anchor in the register holds to its words
Binaries, clients and the SDK
What is shipped and run. A binary is not a ledger dimension — the ledger keys on settings, operations, status subsystems and console routes, which are what the binary CARRIES — so its evidence is its packages' floors and the rehearsal that drives it.
| Capability | Unit floor | Ledger tiers | Rehearsal | Mutations | Composed smoke |
|---|---|---|---|---|---|
| authboxd authboxdHTTPS over mutual TLS · RFC 5280, RFC 8446 | cmd/authboxd 75 (all) internal/server 90 internal/config 85 internal/tlsx 90 | unit · integration | 9 | 14 | 2 |
| authboxproxy authboxproxyHTTPS over mutual TLS, forwarding to an application · RFC 5280, RFC 8446 | cmd/authboxproxy 75 (all) internal/proxy 90 | unit · integration · scenario | 26 | 18 | 3 |
| authboxvault authboxvaultHTTPS over mutual TLS · RFC 5280 | cmd/authboxvault 70 (all) internal/vault 80 | not a ledger dimension | 0 | 0 | 3 |
| authboxportal authboxportalHTTPS over mutual TLS · RFC 5280 | cmd/authboxportal 70 (all) internal/portal 80 | unit · integration · federation | 0 | 40 | 7 |
| authboxkas authboxkasthe OpenTDF key access rewrap operation over mutual TLS · OpenTDF 4.3.0 | cmd/authboxkas 70 (all) internal/kas 90 sdk/marked/tdf not in the report | unit · integration | 1 | 12 | 3 |
| authboxldapsync authboxldapsyncLDAP client over LDAPS · RFC 4511, RFC 4513 | cmd/authboxldapsync 35 (all) internal/ldapsync 75 | not a ledger dimension | 1 | 9 | 1 |
| authboxscimsync authboxscimsyncSCIM 2.0 client over HTTPS · RFC 7643, RFC 7644 | cmd/authboxscimsync exempt · unit internal/scimsync 80 | unit only | 3 | 23 | 3 |
| authboxclient authboxclientHTTPS client against the enrolment and administration surfaces · RFC 2986, RFC 5280 | cmd/authboxclient 35 (all) internal/client 85 internal/pki/keystore 90 | not a ledger dimension | 4 | 4 | 2 |
| authbox-agent authbox-agentHTTPS client against the enrolment surface · RFC 2986 | cmd/authbox-agent exempt · integration | not a ledger dimension | 0 | 4 | absent |
| authboxctl authboxctllocal administration of a deployment's own state | cmd/authboxctl 70 (all) | not a ledger dimension | 0 | 0 | 1 |
| authboxjs authboxjsbrowser fetch against the console and administration surfaces | cmd/authbox-sdk exempt · unit | unit · integration · federation | 0 | 3 | absent |
| Object store object-storean S3 subset in, labelled objects out | cmd/authbox-store 50 internal/objectstore 90 internal/authboxkit exempt · unit | not a ledger dimension | 8 | 14 | 6 |
| Dialect sidecar dialect-sidecara customer's own API shape in, the same shape out | cmd/authbox-dialect 20 internal/dialectserve 80 internal/dialect 90 internal/dialectconform 80 | unit · integration | 0 | 22 | 6 |
Served surfaces
What answers on a listener. These are the rows the exercise ledger reaches most directly: a surface has a switch, an operation or a console route, and the ledger keys on all three.
| Capability | Unit floor | Ledger tiers | Rehearsal | Mutations | Composed smoke |
|---|---|---|---|---|---|
| Enrolment intake enrolment-intakeCSR intake over HTTPS · RFC 2986, RFC 5280 | internal/api/enroll 85 internal/pki 85 | unit · integration | 10 | 0 | 2 |
| ACME server acmeACME with device-attest-01 · RFC 8555, draft-acme-device-attest | internal/acme 80 | unit · integration · scenario · federation | 4 | 16 | 1 |
| EST server estEnrollment over Secure Transport · RFC 7030 | internal/est 85 | unit · integration · federation | 1 | 3 | 2 |
| Invitation mail invitation-mailSMTP submission to the organization's relay · RFC 5321 | internal/vault 80 internal/smtpsink exempt · integration | unit · integration | 2 | 7 | 2 |
| Credential claim credential-claimHTTPS with no client certificate | internal/vault 80 | unit · integration | 0 | 0 | 1 |
| OCSP responder ocsp-responderOCSP over HTTP · RFC 6960 | internal/ocsp 80 | unit · integration · omni · federation | 1 | 7 | 2 |
| Administration API admin-apiHTTPS over mutual TLS · OpenAPI 3.1 | internal/api/admin 85 internal/server 90 | unit · integration · federation | 8 | 12 | 2 |
| Console consoleserver-rendered HTML over mutual TLS · OpenAPI 3.1 | internal/ui 85 internal/consoleproject 95 | unit · integration · scenario · federation | 8 | 32 | 3 |
| Brokerage brokeragemission brokerage over HTTPS · OpenAPI 3.1 | internal/api/brokerage 80 | unit · integration · federation | 2 | 33 | 4 |
| Clearance authority clearanceclearance question over HTTPS · OpenAPI 3.1 | internal/api/clearance 85 | unit · integration · omni | 1 | 12 | 2 |
| self selfself-description over HTTPS · OpenAPI 3.1 | internal/api/self 85 | unit · integration · omni · federation | 0 | 14 | 1 |
| Standing agreements agreementsHTTPS over mutual TLS · OpenAPI 3.1 | internal/portal 80 | unit · integration · federation | 0 | 16 | 3 |
| SAML identity provider saml-providerSAML 2.0 Web Browser SSO, HTTP-Redirect and HTTP-POST bindings, signing only · SAML 2.0 Core, SAML 2.0 Bindings, SAML 2.0 Metadata, XML Signature, Exclusive XML Canonicalization 1.0 | internal/saml 90 | unit only | 2 | 23 | 2 |
| OIDC provider oidc-providerOpenID Connect authorization code flow with PKCE · OpenID Connect Core 1.0, RFC 8705, RFC 7636 | internal/oidc 85 | unit · integration · federation | 1 | 6 | 1 |
| AuthZEN PDP authzenOpenID AuthZEN Authorization API · OpenID AuthZEN Authorization API 1.0 | internal/api/authzen 95 | unit · integration · federation | 0 | 4 | 2 |
| Shared signals transmitter shared-signalsOpenID Shared Signals Framework, RFC 8936 poll, RFC 8417 tokens · RFC 8417, RFC 8936, RFC 9493, OpenID CAEP 1.0, OpenID RISC 1.0 | internal/ssf 80 | unit · integration | 0 | 20 | absent |
| LDAPS directory ldaps-directoryLDAP v3 over TLS, read-only, SASL EXTERNAL bind · RFC 4511, RFC 4513 | internal/ldapserve 80 | unit · integration · federation | 2 | 22 | 3 |
| The federation's names federation-namesauthoritative DNS over UDP and TCP, with DNSSEC signing · RFC 1035, RFC 4034, RFC 4035 | internal/names 95 internal/dnsserve 80 | unit · integration · scenario · federation | 0 | 29 | 4 |
| The anonymous door anonymous-doormatch, strip, forward — no decision and no injected identity | internal/proxy 90 | unit · integration · scenario | 0 | 1 | 2 |
| The front door's directory front-door-directoryone HTML page, GET, no client certificate — drawn from the route table | internal/proxy 90 internal/authboxkit exempt · unit | unit · scenario | 0 | 3 | absent |
| Authorized streams streamslabelled frames over one long-lived request, fanned out by marking | internal/stream 80 internal/proxy 90 | unit · integration | 7 | 13 | absent |
| The marked response markedone response header carrying a marking, compared against the caller's chain | internal/proxy 90 sdk/marked not in the report | unit only | 0 | 14 | 3 |
| SSH through the door ssh-through-the-doora raw connection wrapped in mutual TLS, routed by SNI, spliced unread · RFC 4253 | internal/splice 95 internal/proxy 90 | unit only | 0 | 6 | absent |
| Public listener public-listenerHTTPS with no client certificate requested | internal/api/public 85 | unit only | 0 | 0 | 2 |
| Embedded documentation embedded-docsthe accreditation collection rendered into the binary | internal/docs 90 internal/docrender 90 | unit · integration · scenario · federation | 0 | 5 | absent |
| Health healthliveness and readiness over HTTPS | internal/health 95 | unit only | 0 | 1 | 2 |
| Metrics metricsPrometheus text exposition | internal/telemetry 90 | unit · integration · omni | 1 | 4 | absent |
| Status and topology deployment-statusthe deployment's own state, computed and drawn | internal/status 95 internal/topology 95 | unit · integration · scenario · federation | 0 | 8 | 2 |
| SSH certificate authority ssh-certificate-authorityOpenSSH certificates (PROTOCOL.certkeys) and revocation lists (PROTOCOL.krl) · RFC 4251, RFC 5656 | internal/sshcert 85 internal/pki 85 internal/api/enroll 85 | unit · integration · scenario | 1 | 16 | absent |
| The jump door jump-doorSSH — an SSH server on the front door that a client jumps through, one direct-tcpip channel per decision · RFC 4253, RFC 4252, RFC 4254 | internal/jumpdoor 95 internal/proxy 90 internal/sshcert 85 internal/splice 95 | unit · integration | 0 | 6 | absent |
Subsystems
What is inside the box. A subsystem's ledger tiers come from its status keys, which is why a subsystem nothing reports on shows no tier however well its package is covered.
| Capability | Unit floor | Ledger tiers | Rehearsal | Mutations | Composed smoke |
|---|---|---|---|---|---|
| Registration authority registration-authorityPKCS#10 forwarded over EST or ACME to the organisation's own CA · RFC 7030, RFC 8555, RFC 2986 | internal/pki/ra 70 internal/pki 85 | unit · integration | 0 | 6 | absent |
| Enrolment invitations invitationssingle-use expiring token | internal/invite 90 | unit · integration · federation | 10 | 0 | 1 |
| The door follows the project door-follows-projectroute records derived from the signed bundle a door already polls | internal/dataset 90 internal/proxy 90 internal/replica 90 internal/credential 95 internal/api/admin 85 internal/api/enroll 85 internal/portal 80 | unit · integration · federation | 0 | 4 | 4 |
| Service certificates service-certificatesderived identity plus a bounded, single-use invitation | internal/dataset 90 internal/pki 85 internal/api/admin 85 internal/api/enroll 85 internal/client 85 internal/credential 95 internal/proxy 90 internal/portal 80 internal/acme 80 internal/vault 80 | unit · integration · federation | 0 | 6 | 10 |
| Attested custody attested-custodyrecorded key-custody claim on an issued credential | internal/attestrecord 100 | unit · integration | 2 | 11 | 2 |
| Device attestation device-attestationkey-attestation statements verified against manufacturer roots · draft-acme-device-attest | internal/attestverify 95 | unit · integration | 2 | 11 | 2 |
| CA hierarchy ca-hierarchyX.509 issuance · RFC 5280 | internal/pki 85 internal/pki/keystore 90 | unit · integration | 0 | 8 | 2 |
| CRL distribution crl-distributionX.509 certificate revocation lists · RFC 5280 | internal/pki 85 | unit · integration · federation | 1 | 8 | 1 |
| OCSP client ocsp-clientOCSP over HTTP against an upstream CA · RFC 6960 | internal/ocsp 80 | unit · integration | 2 | 7 | absent |
| Post-quantum issuance post-quantumML-DSA certificates alongside the classical set · FIPS 204 | internal/pki 85 | unit only | 0 | 1 | absent |
| PKCS#12 export pkcs12-exportPKCS#12 with PBES2 and an SHA-256 HMAC · RFC 7292, RFC 8018 | internal/pkcs12 85 | not a ledger dimension | 0 | 4 | 1 |
| Short-lived profile short-lived-profilecertificate profiles with a validity measured in hours · RFC 5280 | internal/pki 85 | unit · integration | 1 | 2 | 2 |
| Entities and groups entities-and-groupsX.500-shaped directory of subjects · RFC 4514 | internal/dataset 90 internal/identity 90 | unit · integration · omni · federation | 7 | 27 | 2 |
| Dynamic group membership members-everyonea declared membership, resolved at load into the ordinary member list | internal/dataset 90 internal/authz 90 | not a ledger dimension | 0 | 9 | absent |
| Missions missionsnamed requirements over a subject's standing | internal/authz 90 | unit · integration · omni · federation | 18 | 30 | 3 |
| Data markings data-markingsOpenTDF attribute URIs · OpenTDF 4.3.0 | internal/opentdf 90 | unit · integration | 13 | 5 | 3 |
| Obligations obligationsstanding compliance questions over the store | internal/obligation 95 | unit · integration · scenario · federation | 0 | 3 | 1 |
| Goals goalsobligation reports joined over a project tree | internal/goal 80 | unit · integration · scenario · federation | 0 | 6 | absent |
| Delegated identity (XPE) xpeX-ProxiedEntitiesChain and X-ProxiedIssuers-Chain | internal/xpe 95 | unit · integration · omni · federation | 0 | 14 | 2 |
| WebAuthn step-up webauthnWebAuthn assertion as a second signature · W3C WebAuthn Level 2 | internal/webauthn 85 | unit · integration · scenario · federation | 1 | 6 | absent |
| Signed actions signed-actionsactor signature over one action, and a periodic chain-head countersignature · RFC 7515 | internal/attest 85 | unit · integration · omni · federation | 0 | 13 | 1 |
| Decision receipts receiptsJWS over one permitted decision · RFC 7515 | internal/receipt 95 | unit · integration · federation | 14 | 9 | 3 |
| Authorization engine authorization-enginethe specification IS the authorization map · OpenAPI 3.1 | internal/authz 90 internal/spec 95 internal/conformance 85 | unit · integration · federation | 7 | 4 | 2 |
| Activity projection activitya projection over the decision record and this process's own counters | internal/activity 90 | unit · integration · scenario · federation | 0 | 12 | absent |
| Entity history entity-historya projection over records that already exist | internal/history 90 | unit · integration · scenario · federation | 3 | 6 | 3 |
| SPIFFE federation spiffe-federationX509-SVID peers from declared foreign trust domains · SPIFFE X509-SVID | internal/federation 95 internal/spiffeid 85 | unit · integration · federation | 0 | 5 | 1 |
| Foreign-schema codec seam foreignseam between AuthBox's model and a foreign one | sdk/foreign not in the report internal/foreign 90 | not a ledger dimension | 0 | 9 | absent |
| STANAG label seam stanagseam between a NATO confidentiality label and this dictionary · STANAG 4774, STANAG 4778 | internal/stanag 90 | not a ledger dimension | 0 | 14 | absent |
| Replicas replicassigned dataset bundles with a monotonic serial | internal/replica 90 | unit · integration · federation | 1 | 4 | 3 |
| Replica publish replica-publishsigned replica bundle of the live store, on a cadence, served on request | internal/replica 90 | unit · integration · scenario · federation | 0 | 27 | 2 |
| Sync engine and live cascade sync-engineauthority bundles, adopted from an upstream and served per consumer | internal/syncengine 95 internal/authoritybundle 75 internal/authorityserve 80 | unit · integration · federation | 0 | 26 | 4 |
| Project authority federation project-authoritya project owned by another AuthBox, with a freshness budget | internal/upstream 75 | unit · integration · federation | 0 | 9 | 1 |
| Org attribute authorities org-attribute-authoritiessigned assertions over an attribute name somebody else owns | internal/authoritybundle 75 | unit · integration · omni · federation | 0 | 0 | 2 |
| Kubernetes ingress mode proxy-kuberneteslist and watch over this cluster's Services | internal/proxy 90 | unit · integration · scenario | 0 | 17 | absent |
| Self-enrolling credential managed-credentialthe companion enrols and renews its own certificate | internal/credential 95 internal/credential/selfenroll 80 | unit only | 7 | 0 | 2 |
| Audit chain audit-chainappend-only hash-chained records, sealed into segments | internal/audit 95 | unit · integration · omni · federation | 7 | 5 | 3 |
| Signed audit export audit-exporta sealed segment turned into an artifact a SIEM can prove it received | internal/auditexport 80 | not a ledger dimension | 0 | 4 | 2 |
| Front-door audit hand-off door-audit-handoffone plan-055 signed export per sealed segment, POSTed in ordinal order | internal/auditexport 80 internal/activity 90 | unit · integration · federation | 7 | 5 | 2 |
| Transparency log transparency-logstatic tile tree with signed-note checkpoints · C2SP tlog-tiles, C2SP signed-note | internal/tlog 90 | unit · integration | 0 | 6 | 2 |
| Backup and restore backup-restorea manifest-wrapped tar of the dataset, the audit segments and the keystore | internal/backup 75 | unit · integration | 1 | 5 | absent |
| Policy export policy-exportthe declared requirements as Rego and Cedar | internal/policycodec 90 | unit · integration | 0 | 5 | absent |
| Control mapping and OSCAL controlsNIST 800-53 control mapping, emitted as an OSCAL component definition · NIST SP 800-53 Rev. 5, OSCAL 1.1 | internal/assurance 75 | integration | 0 | 2 | absent |
| Operational log operational-logstructured operational logging | internal/telemetry 90 | unit · omni | 0 | 4 | absent |
| Store backends store-backendsmemory, file, PostgreSQL and MySQL behind one repository interface | internal/store 75 internal/store/file 75 internal/store/memory 95 internal/store/sqlstore exempt · db internal/store/sqlstore/postgres exempt · db internal/store/sqlstore/mysql exempt · db | unit · integration · federation | 0 | 9 | 3 |
| The Register — AuthBox's own design system design-systemone stylesheet and three embedded faces in, every door AuthBox draws out | internal/authboxkit exempt · unit | not a ledger dimension | 0 | 6 | absent |
| A day in the harbour watch walkthroughsix acts over a running federated composition, asserted as it goes | — | not a ledger dimension | 0 | 1 | 6 |
Build-time tools
What this repository's own claims depend on. Nothing here runs in a deployment, so nothing here is a ledger dimension or a rehearsal act; the floor and the mutations are the whole of the proof.
| Capability | Unit floor | Ledger tiers | Rehearsal | Mutations | Composed smoke |
|---|---|---|---|---|---|
| Documentation and register renderer docs-rendererregisters in, generated documents out | cmd/authbox-docs exempt · unit | not a ledger dimension | 0 | 15 | absent |
| The mark and the tool that derives it brand-markdelivered artwork in, the forms every surface serves out | cmd/authbox-brand 85 internal/brand 90 | not a ledger dimension | 0 | 0 | absent |
| Mutation harness mutation-harnessapply a declared deletion, require the named tests to fail | cmd/authbox-assure exempt · unit | not a ledger dimension | 0 | 12 | absent |
| Release evidence report evidence-reporteach gate's own machine-readable output, assembled | cmd/authbox-testreport exempt · unit internal/testreport 90 | not a ledger dimension | 0 | 6 | absent |
| Benchmark regression gate bench-gatetwo `go test -bench` runs compared | cmd/authbox-benchcompare exempt · unit internal/benchcompare 90 | not a ledger dimension | 0 | 6 | absent |
| Software bill of materials sbomCycloneDX-shaped JSON built from the build itself · CycloneDX 1.5 | cmd/authbox-sbom exempt · unit internal/sbom 85 | not a ledger dimension | 0 | 5 | absent |
| Release signing release-signinga detached signature over the release's SHA256SUMS | cmd/authbox-sign exempt · unit internal/relsign 85 internal/changelog 85 internal/provenance 80 | not a ledger dimension | 0 | 12 | absent |
| Release courier bundle release-mediaone tar archive with a signed MANIFEST naming every file's digest and posture | cmd/authbox-release exempt · unit internal/relbundle 85 internal/relimages 90 | not a ledger dimension | 0 | 13 | absent |
| Reference stream sink stream-sinkverified frames in, receipts and frame hashes on disk | cmd/authbox-ingest 25 | not a ledger dimension | 7 | 13 | 1 |
| Local S3 shim store-shimloopback S3 in, mutual TLS out | cmd/authbox-store-shim 25 | not a ledger dimension | 0 | 0 | absent |
| Marked-response showcase showcase-recordssix classified records, every response labelled, and a TDF export of each | cmd/authbox-showcase-records 55 | not a ledger dimension | 0 | 22 | 2 |
| OIDC login showcase showcase-oidca relying party's discovery, PKCE authorization code and RFC 8705 mTLS token exchange | cmd/authbox-showcase-oidc 50 | not a ledger dimension | 1 | 0 | 2 |
| SAML service provider showcase showcase-samla service provider's SP metadata, HTTP-Redirect AuthnRequest and POST-binding assertion consumer, with signature verification | cmd/authbox-showcase-saml 65 | not a ledger dimension | 2 | 23 | 1 |
| Fixture PKI and demonstration data fixture-dataa fixture hierarchy and a curated demonstration organization | cmd/authbox-testpki 30 (all) cmd/authbox-demogen 85 internal/testpki 85 internal/testkit exempt · integration | not a ledger dimension | 1 | 3 | 2 |
| Rehearsal population rehearsala population file, a deterministic schedule, and a run log of acts against a deployment's own doors | cmd/authbox-simulate exempt · unit internal/simulate 50 | not a ledger dimension | 1 | 12 | absent |
| Compose-to-Kubernetes translation compose-translationa rendered `docker compose config` document translated to Kubernetes objects | cmd/authbox-kube exempt · unit internal/composekube 90 | not a ledger dimension | 0 | 3 | absent |
| Scanner gate and suppression register scan-gatefive scanners' native JSON, judged against one register | cmd/authbox-scan 80 internal/scanreg 85 | not a ledger dimension | 0 | 5 | absent |
This deployment’s customer dialects
2 dialect(s), proved — 3 mapped operation(s), 1 of which this deployment can be asked. 62 generated instance(s) were translated and checked against the customer’s own document: 59 translated, 3 refused for carrying no value a required field needed, and 0 refused by the document they were translated into. A dialect is a customer’s own API shape brought as their OpenAPI document, and a mapping of five rule kinds onto it — no expression, no conditional and no code — proved at load against both documents.
| Dialect | Declared by | Customer document | Operations | Answerable here | Instances |
|---|---|---|---|---|---|
| tideline-gateway/1 deploy/all-in-one/dialect | the all-in-one composition | Tideline Access Gateway API 1.1 sha256 2c79635e44d6 | 1 | 1 | 28 |
| acme-iam/1 internal/dialect/testdata/acme-iam | internal/dialect's own test fixture | Acme IAM Access API 2.4 sha256 7921dbd858e7 | 2 | 0 | 34 |
How to read it
- Capability
- The row's name, its id in the capability register — the name the console's Services page, the exercise ledger and the support matrix all use for the same row — what it speaks, and the standards it speaks it by.
- Unit floor
- Every package the row declares, with the statement-coverage floor the gate holds it to. (all) marks a floor held against the all-tiers measurement, which folds the compiled binaries in and is not comparable with a unit-report floor. exempt · tier names the tier a package's proof lives in instead. not in the report is a package the coverage report does not measure — the generated SDK, which has no statement coverage here at all.
- Ledger tiers
- Every tier that reaches any of the row's settings, status subsystems, specification operations or console route. unit only is a row the ledger knows at that tier and no other. not a ledger dimension is a row the ledger cannot key on — a binary or a build-time tool — and is a statement about the ledger rather than about the row.
- Rehearsal
- How many behaviours of the shipped population drive this capability against a live deployment; hover the number for their names. Each behaviour carries an act kind, and one declared table maps an act kind to the capabilities it exercises. Four rows are credited with the run itself rather than with a behaviour, because the rehearsal, its fixture data, the metrics it reads back and the daemon every act talks to are what a run is rather than something a behaviour does.
- Mutations
- How many declared mutations prove the rules of this row's plans are not vacuously asserted. Zero is printed as itself: a capability whose plans made no ruling anybody mutated is a finding, not a blank.
- Composed smoke
- How many check lines of the composed all-in-one bring-up name this capability; hover the number for their text. The corpus is every deploy/all-in-one script plus the makefile's own all-in-one, rehearsal and kind recipes, and a check line is one that prints an OK — what a step says when it held. Each is counted because the row declares an anchor for it: an exact fragment of that line, which a test proves still appears there, so a step that is deleted or reworded drops out of this column instead of being claimed by a row nobody re-read. absent means no check line names this capability — the honest state for the SSH capabilities, the OCSP client, policy export, the post-quantum profile and the build-time tools, which a composed bring-up does not exercise — and is a different statement from a zero, which would read as a measurement.
These columns sample a ladder of tiers — unit, deploy-tier (the static facts of what is shipped: compose files, configurations, dataset fragments, the smokes' own shell helpers, the specification read beside any of them), integration, scenario and omni, the composed smoke, the rehearsal — and where a claim sits on it is part of the claim: a fact that could be read off a checked-in file but is proved only in the composed-smoke column is a proof that costs twenty-five minutes to re-run.
What this page deliberately does not carry is a measured coverage percentage. That figure is the output of a run and not a property of the repository, so a page generated from it would be stale on the next commit. It lives in the release evidence report, assembled at a tag. The floor is the claim a gate holds, and the floor is what is printed here.
Generated from the registers on every documentation run. The same table, with its legend, is beside the support matrix in the technical collection.